Federal Agencies Warn: Increased Phishing Targets Government Data Q2 2026
Federal agencies have issued a stark warning regarding an anticipated increase in sophisticated phishing attacks targeting government data in Q2 2026, urging heightened vigilance and robust defensive measures across all departments.
Por: Marcelle em 23 de setembro de 2026
Federal agencies have issued a critical warning regarding an anticipated surge in sophisticated phishing attempts specifically targeting government data during Q2 2026, necessitating immediate and enhanced cybersecurity protocols.
A significant cyberattack alert: federal agencies issue warning on increased phishing attempts targeting government data in Q2 2026, signaling a critical period for national cybersecurity. This proactive advisory underscores the evolving threat landscape and the imperative for robust defense mechanisms to safeguard sensitive information from increasingly sophisticated adversaries.
Understanding the Escalating Phishing Threat
The digital frontier is constantly shifting, presenting new challenges for cybersecurity professionals. Federal agencies are now sounding the alarm, projecting a substantial increase in phishing attacks aimed squarely at government data in the second quarter of 2026. This isn’t merely a speculative forecast; it’s based on intelligence gathered from various sources, indicating a concerted effort by malicious actors to compromise critical systems.
Phishing, a well-established cyber threat, has evolved far beyond simple email scams. Attackers are employing highly personalized and sophisticated techniques, often leveraging artificial intelligence and deepfake technology to craft convincing lures. These advanced methods make it increasingly difficult for even trained personnel to identify and thwart attacks.
Sophistication of Modern Phishing Attacks
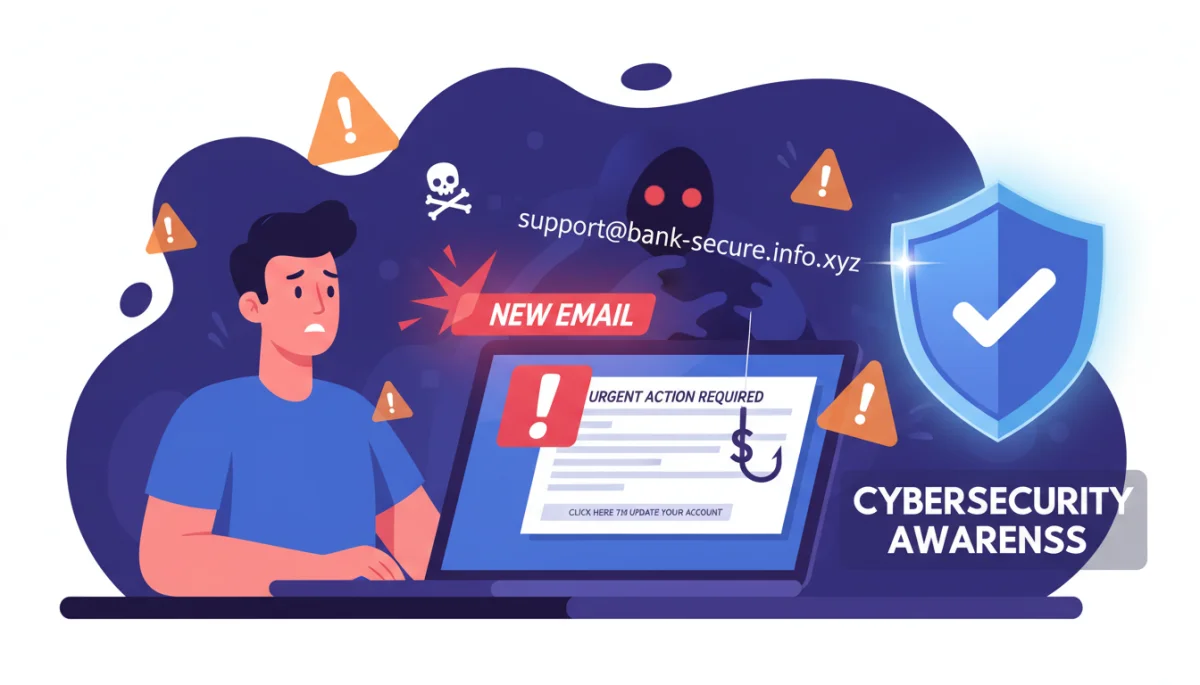
Modern phishing campaigns are characterized by their precision and psychological manipulation. They often mimic legitimate communications from trusted sources, exploiting human vulnerabilities rather than just technical ones. This includes spear-phishing, whaling, and smishing (SMS phishing), each designed to trick specific individuals or high-value targets into revealing sensitive information or granting unauthorized access.
Personalized Content: Attackers research targets to create emails or messages that appear highly relevant.
Social Engineering: Exploiting trust and urgency to bypass critical thinking.
Multi-Channel Attacks: Phishing attempts spread across email, SMS, social media, and even voice calls.
AI-Powered Lures: Using AI to generate highly convincing text and imagery, making detection harder.
The projected increase in Q2 2026 suggests a new level of coordination and resource allocation by threat actors. This period could see a confluence of geopolitical events, technological advancements, and strategic timing, all contributing to a heightened risk environment for government data. Agencies must prepare not just for more attacks, but for more intelligent and adaptable ones.
The escalating nature of these threats demands a multi-faceted approach, combining technological defenses with continuous human education. Understanding the adversary’s methods is the first step in building an effective counter-strategy. The federal warning serves as a crucial call to action for all involved in protecting public sector information.
Key Vulnerabilities Exploited by Phishing Campaigns
Phishing attacks often succeed by targeting specific weaknesses within an organization’s security posture, encompassing both technological gaps and human factors. Federal agencies, due to the sheer volume and sensitivity of data they handle, present particularly attractive targets. The upcoming surge in Q2 2026 is expected to capitalize on these known vulnerabilities with renewed intensity.
One primary vulnerability is the human element. Even with advanced security systems, an employee clicking on a malicious link or opening an infected attachment can compromise an entire network. Attackers meticulously craft their messages to bypass initial technical filters and then rely on human error or lack of awareness to achieve their objectives.
Technological Weaknesses and Entry Points
Beyond human factors, technological shortcomings also play a significant role. Outdated software, misconfigured systems, and insufficient network monitoring can create exploitable entry points for sophisticated phishing campaigns. Attackers often scan for these vulnerabilities, using them as pathways to deliver their malicious payloads or gain initial access.
Unpatched Software: Exploiting known vulnerabilities in operating systems, applications, and plugins.
Weak Authentication: Lack of multi-factor authentication (MFA) or reliance on easily guessed passwords.
Insufficient Email Filters: Ineffective spam and phishing filters allowing malicious emails to reach inboxes.
Shadow IT: Unauthorized software or services creating unmonitored entry points.
Another critical area of vulnerability lies in supply chain attacks. Compromising a third-party vendor or partner can provide an indirect route into a federal agency’s network. Phishing attacks against these entities can be just as damaging, if not more so, as they often go unnoticed for longer periods.
Addressing these vulnerabilities requires a holistic strategy that integrates cutting-edge technology with comprehensive training programs. Proactive vulnerability assessments and penetration testing are essential to identify and mitigate potential weaknesses before attackers can exploit them. The federal warning highlights the urgency of closing these gaps well in advance of the anticipated Q2 2026 surge.
Protecting Government Data: Essential Strategies
Given the imminent threat of increased phishing attempts targeting government data in Q2 2026, federal agencies must implement and reinforce a robust set of protective strategies. These measures need to be comprehensive, addressing both technological defenses and human preparedness to create a resilient cybersecurity posture.
At the core of any effective defense is a multi-layered security approach. No single solution can guarantee complete protection against sophisticated phishing. Instead, a combination of preventative, detective, and responsive controls is necessary to minimize risk and mitigate potential damage.
Implementing Advanced Security Protocols
Technological safeguards form the first line of defense. Agencies should prioritize the deployment and continuous updating of advanced security tools designed to detect and block phishing attempts. This includes next-generation firewalls, intrusion detection/prevention systems, and endpoint detection and response (EDR) solutions.
Multi-Factor Authentication (MFA): Mandating MFA for all access points, especially for sensitive systems.
Email Gateway Security: Advanced filters that use AI and machine learning to identify and quarantine suspicious emails.
Data Loss Prevention (DLP): Tools to prevent sensitive data from leaving the network through unauthorized channels.
Regular Patch Management: Ensuring all systems and software are up-to-date with the latest security patches.
Beyond technology, continuous training and awareness programs for all personnel are paramount. Employees are often the weakest link, but with proper education, they can become the strongest defense. Simulations of phishing attacks, regular security briefings, and clear reporting mechanisms are vital.
Furthermore, incident response plans must be well-defined, regularly tested, and readily available. Knowing how to react swiftly and effectively to a breach can significantly reduce its impact. This includes clear communication protocols, forensic investigation capabilities, and recovery strategies.
The Role of Employee Training and Awareness
While technological defenses are crucial, the human element remains a primary target for phishing attacks. Therefore, comprehensive and continuous employee training and awareness programs are indispensable for federal agencies to counter the projected surge in Q2 2026. An informed workforce acts as a critical line of defense against sophisticated social engineering tactics.
Effective training goes beyond simply telling employees not to click on suspicious links. It involves fostering a culture of cybersecurity awareness where every individual understands their role in protecting sensitive government data. This requires engaging content, regular refreshers, and practical exercises that simulate real-world threats.
Building a Cyber-Aware Culture
A strong cybersecurity culture is built on consistent education and clear communication. Training programs should be tailored to different roles within the agency, recognizing that executives, IT staff, and general employees face varying types of threats and have different levels of access. The goal is to empower employees to identify and report potential phishing attempts without fear of reprimand.
Phishing Simulations: Regular, realistic phishing exercises to test employee vigilance and identify training gaps.
Interactive Workshops: Hands-on sessions demonstrating common phishing techniques and effective countermeasures.
Clear Reporting Channels: Establishing easy and anonymous ways for employees to report suspicious emails or activities.
Continuous Education: Providing ongoing updates on new threats and best practices through newsletters, alerts, and micro-learnings.
The effectiveness of training should be measured and refined. Tracking participation rates, phishing click-through rates in simulations, and reported incidents can provide valuable insights into program efficacy. This data can then be used to target specific areas for improvement and ensure that training remains relevant and impactful.
Ultimately, a well-trained workforce is an agency’s most valuable asset in the fight against cyber threats. By investing in robust employee awareness programs, federal agencies can significantly reduce their attack surface and enhance their overall resilience against the anticipated phishing onslaught in Q2 2026.
Federal Agencies’ Collaborative Response
Responding to a threat as pervasive as increased phishing attempts targeting government data requires a unified and collaborative effort among federal agencies. The warning for Q2 2026 is not just an individual agency’s concern, but a collective challenge demanding coordinated strategies and shared intelligence across the entire government landscape.
Inter-agency cooperation is vital for pooling resources, sharing threat intelligence, and developing standardized best practices. This collaborative approach ensures that lessons learned by one agency can quickly benefit others, creating a stronger, more cohesive defense against common adversaries.
Cross-Agency Information Sharing
One of the most critical aspects of a collaborative response is the timely and effective sharing of threat intelligence. Agencies need mechanisms to communicate details about new phishing campaigns, attack vectors, and indicators of compromise (IOCs) as soon as they are identified. This allows other agencies to proactively update their defenses and warn their personnel.
Joint Task Forces: Establishing specialized groups focused on specific cyber threats, including phishing.
Information Sharing and Analysis Centers (ISACs): Leveraging existing platforms for real-time threat intelligence exchange.
Standardized Protocols: Developing common frameworks for incident reporting and response across all federal entities.
Joint Training Exercises: Conducting simulated cyberattacks involving multiple agencies to test coordination and response.
Beyond information sharing, collaboration extends to policy development and resource allocation. Agencies can work together to advocate for enhanced cybersecurity funding, develop unified policies that strengthen defenses across the board, and leverage shared services for security solutions, reducing duplication of effort and maximizing efficiency.
The federal warning for Q2 2026 underscores the necessity of this collaborative spirit. By acting as a united front, federal agencies can present a much more formidable challenge to cyber adversaries, protecting not only their individual data but also the collective security of national information assets.
Future Outlook and Long-Term Cybersecurity Resilience
The warning about increased phishing attempts targeting government data in Q2 2026 serves as a stark reminder that cyber threats are a persistent and evolving challenge. Building long-term cybersecurity resilience requires a forward-thinking approach that anticipates future threats, adapts to technological advancements, and fosters a culture of continuous improvement.
Resilience in cybersecurity is not just about preventing attacks; it’s also about the ability to withstand, detect, and rapidly recover from successful breaches. This holistic view acknowledges that perfect prevention is unattainable and focuses on minimizing impact and ensuring business continuity.
Adapting to Emerging Threats
The landscape of cyber threats is constantly shifting, driven by technological innovations and geopolitical dynamics. Federal agencies must invest in research and development to understand emerging threats, such as those leveraging advanced AI, quantum computing, or new forms of social engineering. Staying ahead of adversaries requires proactive intelligence gathering and predictive analysis.
AI-Powered Defenses: Utilizing artificial intelligence and machine learning for anomaly detection and threat prediction.
Zero Trust Architecture: Implementing security models that assume no user or device can be trusted by default, regardless of location.
Quantum-Resistant Cryptography: Researching and developing cryptographic methods that can withstand future quantum computing attacks.
Automated Security Operations: Leveraging automation for faster threat detection, response, and remediation.
Beyond technology, fostering a culture of adaptability and continuous learning within the cybersecurity workforce is crucial. The skills required to defend against cyberattacks are constantly changing, necessitating ongoing training and professional development for security personnel.
Ultimately, building long-term cybersecurity resilience is an ongoing journey, not a destination. The Q2 2026 warning is a critical milestone in this journey, prompting agencies to reassess their strategies and commit to sustained investment in people, processes, and technology to protect government data for years to come.
Key Point
Brief Description
Phishing Surge Q2 2026
Federal agencies warn of significant increase in sophisticated phishing attacks targeting government data.
Advanced Tactics
Attackers use AI, social engineering, and multi-channel approaches for highly personalized lures.
Employee Training Critical
Continuous awareness programs and simulations are essential to empower staff against threats.
Collaborative Defense
Inter-agency information sharing and joint strategies are vital for a unified federal response.
Frequently asked questions about federal phishing warnings
What is the primary concern of the federal agencies’ warning?▼
The main concern is a projected surge in sophisticated phishing attempts specifically targeting government data during Q2 2026. These attacks are expected to be more advanced, leveraging AI and social engineering to compromise sensitive information.
How have phishing techniques evolved recently?▼
Phishing has evolved to include highly personalized content, advanced social engineering tactics, and multi-channel delivery. Attackers now use AI to create convincing lures, making it harder for individuals to distinguish legitimate communications from malicious ones.
What are the key vulnerabilities that attackers exploit?▼
Attackers primarily exploit human error, such as clicking malicious links, alongside technological weaknesses like unpatched software, weak authentication, and inadequate email filtering. Supply chain vulnerabilities also present significant risks.
What measures are federal agencies implementing to counter this threat?▼
Agencies are focusing on advanced security protocols like MFA, robust email gateway security, and data loss prevention. Crucially, they are also emphasizing continuous employee training, phishing simulations, and collaborative intelligence sharing among departments.
Why is inter-agency collaboration important in this context?▼
Collaboration is vital for pooling resources, sharing real-time threat intelligence, and developing standardized best practices. A unified front allows agencies to proactively adapt defenses, warn personnel, and present a stronger collective defense against sophisticated cyber adversaries.
Conclusion
The federal agencies’ warning regarding increased phishing attempts targeting government data in Q2 2026 serves as a critical call to action for comprehensive cybersecurity preparedness. This anticipated surge in sophisticated attacks necessitates a multi-faceted defense, combining cutting-edge technological safeguards with robust employee training and a strong culture of awareness. By fostering inter-agency collaboration and continuously adapting to the evolving threat landscape, federal entities can build enduring resilience, safeguarding vital national information assets against persistent and intelligent adversaries.